Making Software
← All Episodes
Episode 9·September 30, 2026·00:39:00

Episode 9: Inside the Protocol Securing AI Agents at Work

Show Notes

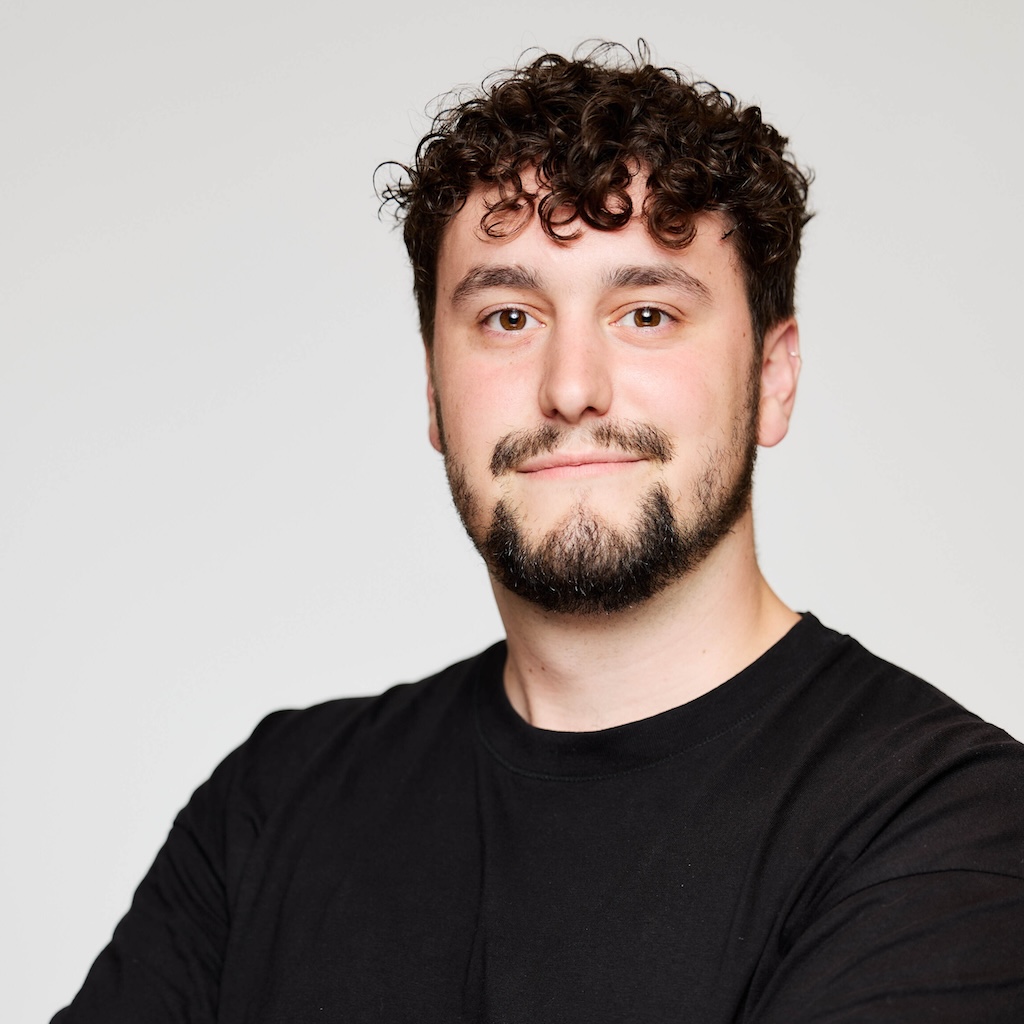
Every time you tell an AI agent to do something and it pops open a browser asking for your permission, you're probably clicking yes without reading it. Miguel Pedregosa is a Senior Software Engineer on the Protocols team at Auth0 (Okta). His team owns the implementation of identity standards inside Auth0 like OAuth, OIDC, SAML, WS-Federation. The infrastructure every developer integrating with Auth0 relies on without thinking about it. Before Auth0, Miguel worked on malvertising detection, tracing malware hidden inside ad traffic. The through line in his career: security-intensive environments where getting it wrong has real consequences. In this episode we talk about what it's like to build infrastructure that millions of developers depend on without knowing it, how Cross-App Access and Enterprise-Managed Auth for MCP came to exist, and what it takes to implement an IETF standard that's still being drafted while industry adoption is already happening. We also get into the difference between what enterprises and startups actually need from identity — and why Miguel thinks basic threat modeling matters even if you never want to touch an RFC. What You'll Learn : Why AI agent auth popups are a security flaw, not just a UX annoyance How Cross-App Access uses an existing enterprise identity provider to let agents authenticate without opening a browserWhat the IDJAG (Identity JWT Assertion Grant) is and why it's the central artifact of the protocolWhat it's like to implement an IETF standard while it's still being drafted — and how Auth0's team fed back into the specThe difference between what enterprises and startups need from identity: legacy system integration at scale- Why basic threat modeling is the minimum for anyone shipping AI agents, and the three questions to start with Resources: Miguel on LinkedIn: https://www.linkedin.com/in/miguel-pedregosa/Cross-App Access blog post: https://auth0.com/blog/setting-up-testing-cross-app-access-auth0/Cross-App Access protocol: https://oauth.net/cross-app-access/IDJAG (Identity JWT Assertion Grant) spec: https://datatracker.ietf.org/doc/html/draft-ietf-oauth-identity-assertion-authz-grantIdentity and Authorization Chaining Across Domains: https://datatracker.ietf.org/doc/draft-ietf-oauth-identity-chaining/

Guest

Miguel Pedregosa

Miguel Pedregosa

Senior Software Engineer, Auth0 (Okta)

Miguel Pedregosa is a Senior Software Engineer at Auth0 working as part of the Protocols team where he focuses on Auth0's core authentication runtime and identity protocol implementations, and their evolution to solve authentication for AI Agents, B2B and B2C at scale. Before Auth0, he has worked on security-sensitive, high-scale projects for the last six years, like the online healthcare platform Ksyos or the malvertisement detector AdSecure. With a Bachelor degree in Computer Science, Miguel finds beauty in giving simple solutions to complex problems focusing always on the human aspect. When he is not thinking about tech, you'll find him playing music or going for a walk in his hometown.

Read the blog post →

Subscribe to Making Software